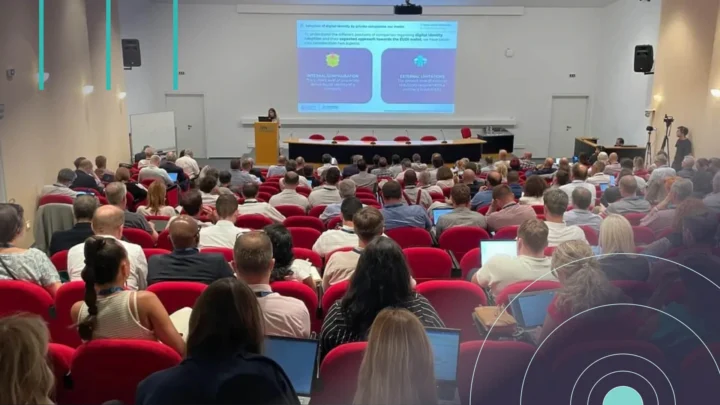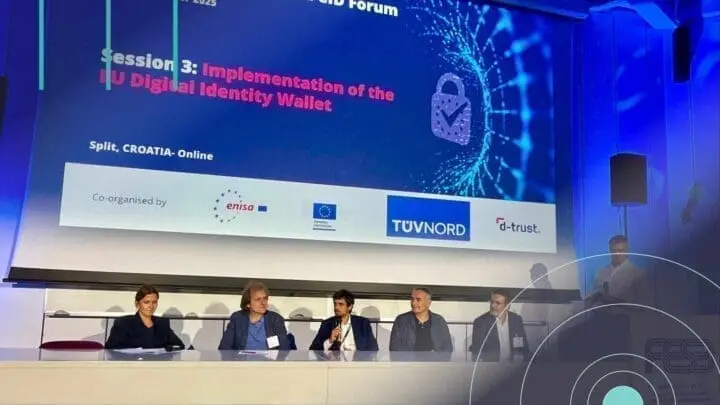
The Global Digital Collaboration (GDC) Conference 2026 brought the digital identity and trust community to Palexpo in Geneva in early September. The Conference was hosted by the Swiss Confederation, co-organised by around forty organisations, and spread across more than 140 sessions in up to eight parallel tracks.
Last October we published ten takeaways from the ENISA Trust Services and eID Forum. That forum is where Europe works through its own agenda in detail. Geneva is a different room: the working assumption there is that digital credentials (passports, licences, payment proofs, professional qualifications…) will have to work across legal systems, not just across borders inside one.
The co-organiser list tells you what kind of event this is: intergovernmental bodies (the European Commission, the ITU, the UNECE, the World Bank, the WHO), standards developers (ISO, IEC, ETSI, CEN-CENELEC, W3C, the FIDO Alliance, the OpenID Foundation, GlobalPlatform, EMVCo, GSMA, the Cloud Signature Consortium), and open-source foundations (the Linux Foundation, the OpenWallet Foundation, LF Decentralized Trust, MOSIP, the Eclipse Foundation), all in the same room.
Day one set the tone. The Swiss Federal Office of Justice opened alongside Brazil’s Minister for Management and Innovation in Public Services and speakers from the airline and platform industries. A Global Digital Collaboration Council panel (with Smart Africa, the Government of Canada, and representatives from finance and technology) argued that public-private leadership is now a prerequisite for this kind of infrastructure, not an optional extra. Sessions ranged from large-scale cross-border wallet pilots, to Smart Africa’s “Sovereign Trust” governance model, to Singapore linking business-registration credentials with Shanghai, to a UNECE/WTO session pricing trade friction at six trillion dollars a year.
Namirial was on the panel “The invisible partners that are indispensable to drive adoption”, alongside providers from across the intermediary community (slides and notes are available on request).
Switzerland’s own position is worth noting because it frames the whole event: its E-ID Act passed by referendum in September 2025 by a very narrow margin; the swiyu wallet has been in public beta since March 2025, now with a separate sandbox for issuers and verifiers to test against; and the production launch has been pushed back to 2027. Switzerland also intends to establish a foundation in Geneva as a permanent home for GDC: neutral ground for a genuinely global conversation.
Below are the ten things we think matter, and what each one means for organisations that will have to operate through this landscape.
1 – Digital identity has stopped being a European regulatory story
Mobile driving licences, digital travel credentials, health certificates now linking more than eighty countries through the WHO, verifiable trade documents, learning credentials, and population-scale identity systems in the Global South were all treated as important subjects, not side cases.
A joint EU-India session made this point precisely. The EU’s Digital Identity Wallet, mandated under Regulation (EU) 2024/1183, and India’s national digital infrastructure were built entirely independently, yet both rest on the same underlying logic: an issuer, a holder, a verifier, a machine-readable registry of who is allowed to issue what, and disclosure of only the attribute needed. The technical formats – SD-JWT VC and ISO mdoc – are becoming a genuine global standard, but the rules for who is accountable when something goes wrong are not global at all. That gap, not the format debate, is the real strategic question for the next three years.
What this means: an organisation building for one jurisdiction today is building on a format that will very likely travel between different countries. The rulebook will not travel with it automatically, so separate planning is needed. This is exactly why our wallet platform is built upon a common issuance and verification core, so a customer isn’t locked into one region’s assumptions.
2 – Standards get you interoperability. They do not get you liability.
Two systems can agree perfectly on how to format and check a credential, and still leave completely open who compensates a bank, a merchant, or a citizen who relied on it and lost money. Inside the EU, eIDAS 2.0 answers this for credentials issued as “qualified”: defined liability, named supervisory bodies, mandatory audits. Outside that boundary, the answer is largely silent.
Geneva’s conference produced a lot of good work on conformance, whether a credential meets a technical specification, through sessions co-run with the OpenID Foundation, the Cloud Signature Consortium and the Commission. Conformance and liability are different questions. A trust registry can confirm an issuer is authorised; however, it cannot tell you who pays when the flow fails.
What this means: if your business model depends on cross-border acceptance, ask early who carries the loss, not just whether the credential will parse. As a qualified trust service provider, liability is something we already carry as part of the supervised chain: it’s built into what a customer buys from us, not an afterthought added after the fact.
3 – The real subject this year was trust registries, not credential formats
Every credential, a passport, a degree, a customs form, a professional licence, depends on one question no format answers by itself: is this issuer actually authorised to issue this, right now? A Trust Registries Task Force (co-led in part by a major platform provider and a national identity program) proposed a federated model: wallet platforms implement trust, but existing national and sector registries keep their authority.
Parallel sessions showed this pattern recurring everywhere: identity, education, travel, trade, business registration; and showed North American and Australasian motor-vehicle authorities negotiating a live mutual-recognition framework for driving licenses, one of the few working precedents for recognition between whole regions. The task force closed by admitting the hardest question is still open: who runs a global trust registry, and on whose authority?
What this means: federation is the right architecture, but someone still has to be the root of trust for any given sector. We already operate inside trust-list infrastructure today (publication, supervision, revocation) so for us this is the operational structure we run on daily, not a future research question.
4 – Having the wallet gateway is not the same as managing the full KYC journey
The dates are what make this concrete. EU member states must make wallets available by 24 December 2026. From 10 July 2027, new anti-money-laundering rules (Regulation (EU) 2024/1624) tighten identity checks. From 24 December 2027, banks, telecoms, public services and very large platforms must accept the wallet wherever strong authentication is legally required, with a supporting register of relying parties in place from the same date.
The result is a very complex system: 27 national wallets, several private ones, four different ways to present a credential, three data formats, one catalogue of credential types and, in financial services alone, on the order of five thousand relying parties who all need to plug in.
A pure connector assumes the credential is already sitting in the wallet, ready to present. Everything before that point (proving who someone is at the right assurance level, connecting to authoritative sources, binding the credential to a phone, handling a lost device, re-verifying when something changes…) is a lifecycle problem, and it is barely solved industry-wide. The signature or seal that makes a transaction legally binding sits at the far end of that same chain, followed by audit and dispute handling.
What this means: whoever owns the whole journey, from onboarding all the way to signature, carries the assurance level the relying party is actually paying for. This is precisely what our platform is structured around: Namirial Onboarding establishes identity at the required assurance level, the Wallet Gateway absorbs the protocol complexity, and our signature services close the transaction. One accountable chain, not five vendors to reconcile after something breaks.
5 – Business wallet: mandated in Europe, incentive-driven elsewhere
One session drew a clean contrast: in Europe, business wallet is arriving because regulation requires it. In the United States, without a comparable mandate, the private sector is building the same capability because it’s commercially useful. Both are replacing manual “know your business” paperwork with instantly verifiable digital records. Whether the two approaches will actually interoperate is genuinely unresolved.
The hard problems are clearly identified: who can delegate authority to whom inside a company, how far below board level that chain of delegation goes, how it plugs into existing access-management systems, and how it connects to authoritative registers such as national company registries. GLEIF’s verifiable Legal Entity Identifier came up repeatedly as a global anchor for corporate identity.
What this means: whichever route gets you there, mandate or incentive, the delegation chain is where liability gets hardest to allocate, because someone has to answer for what an authorised-but-overreaching agent does. This is a core part of what we build into mandate and delegation attestations for businesses, not just individuals.
6 – Signing from a wallet reached the main stage
Two sessions stood out: one on executing qualified electronic signatures directly from a wallet, removing the separate step of buying a standalone certificate; the other, run with the Cloud Signature Consortium and TeleTrusT, on remote and cloud signing architecture aligned with both EU rules and Switzerland’s own signature law, a working example of recognition reaching beyond EU law rather than a hypothetical one.
Presenting a credential proves a fact. Signing creates a legal obligation. Contracts, account openings, mandates and filings all end in a signature, and citizens are meant to get that capability through their wallets. Much of the public conversation about wallets stops at “does the credential check out”, since the transaction itself doesn’t stop there.
What this means: a wallet strategy that ends at verification is incomplete. Our signature services are built to close exactly that gap: turning a verified attribute into a legally binding, auditable signature within the same chain.
7 – Demand has arrived, including from software agents
Age verification ran as a full subject in and of itself, including sessions asking first whether an age check is even warranted before assuming it is. Live demonstrations showed bank-issued age credentials completing an online checkout and a government credential accepted at a physical payment terminal: real transactions, not slideware.
The sharper development was about AI agents acting on people’s behalf. Multiple sessions converged on a single framing worth remembering: Know Your Agent (KYA). It extends “know your business” the way that extended “know your customer”: when a software agent transacts, you need to establish who the agent is, on whose authority it’s acting, and within what limits: verified organisational identity, a bounded and auditable mandate, and evidence of intent that holds up after the fact. An agent can act entirely within a valid mandate and still cause a loss, which is exactly why this is a liability question as much as a technical one.
What this means: any business planning to let agents transact on its behalf, or accept transactions from other people’s agents, needs this identity-and-mandate layer now, not once agents are already live in production. It’s a natural extension of the mandate and delegation work described above, and something we’re already building toward.
8 – Mutual recognition, not harmonization, and a “Europe” wider than the EU
The most consequential outcome of the conference wasn’t a technical spec. A statement of intent toward a pan-European trust framework established a standing collaboration group, explicitly a forum for convening, not a new regulator or standards body.
Its scope is broader than the EU: the EU and European Economic Area, Switzerland, the United Kingdom, Ukraine and other accession candidates, and in principle all forty-six Council of Europe member states. What they share isn’t a single regulation but a common rights framework: the European Convention on Human Rights and Council of Europe data protection standards. The stated design principles favor mutual recognition over central control, privacy by default, open standards, and a model built so it can be exported elsewhere. The evidence behind the push is blunt: an OECD mapping across G7 countries found no single international standard shared by all of them, and a UK survey found nearly four in five digital verification providers naming regulatory diversity as a barrier to working internationally.
What this means: the group is non-binding by design, so its ideas will only matter if institutions and industry actually take them up. We see this as the natural home for the cross-jurisdictional liability terms missing from takeaway two, and we intend to keep engaging with it rather than waiting for a finished standard to implement.
9 – Payments: the wallet becomes an authentication tool, but who’s liable is still open
Payments ran through almost every discussion: card networks and national payment rails on the same panels, account-to-account frameworks, and digital payment credentials discussed from several angles.
The regulatory direction is clear: the European Commission wants the EU wallet treated as equivalent to strong customer authentication under payment rules, and the technical path for that is falling into place. What is not settled is who bears the loss when it fails. The Parliament and Council reached political agreement on the new payment services rules in late November 2025, with the texts published in April 2026; formal publication is expected in the second half of 2026, after which the rules apply about 21 months later, realistically 2028, with the fine detail following from banking regulators after that.
Meanwhile, the industry isn’t waiting: EMVCo has been developing a Digital Payment Credential specification with input from the FIDO Alliance, the OpenID Foundation, the OpenWallet Foundation and W3C. The EPI Initiative has passed fifty million registered users and moved from person-to-person transfers into shops and online checkout, and a digital euro pilot with three dozen payment providers is due to run through the second half of 2027.
What this means: a payment credential only works if issuers, wallets, networks and regulators converge on one shared model rather than several competing ones: this is a place where industry can move ahead of regulation without undermining it. What we bring is the part a payments stack can’t generate for itself: a supervised, liability-bearing chain from identity proofing through to signature.
10 – The European Business Wallet: real opportunity, still being written
The European Business Wallet (EBW) is a genuinely new challenge, not an extension of the personal wallet. Proposed by the Commission on 19 November 2025 as part of a wider digital simplification package, its purpose is to let a company manage who can represent it, exchange official documents through a qualified secure delivery channel, and be found in a Commission-run directory, all anchored to the company’s existing EU identifier. Actions taken through the wallet would carry the same legal weight as actions taken on paper. Crucially, it places no obligation on companies themselves: public bodies must support it, but businesses choose whether to use it, which is exactly why adoption will depend on making the case, not on a mandate.
What this means for us specifically: we haven’t waited for the specification to settle. We’ve been working on business-wallet capability since the early stages: organisational onboarding, mandate and delegation attestations, and seals and qualified signatures for legal entities rather than only individuals. One detail from the Council’s position is worth noting: its move toward requiring prior authorisation and a high level of assurance for providers favors organisations that are already operating under supervision today, rather than new entrants starting from zero.
Namirial’s perspective, in short
Owning the whole journey, from onboarding, credential issuance and verification, to the final signature, audit trail and archiving, matters more than owning one link in the chain. Conformance is close to being solved, but accountability across borders is not, and payments will be the first sensitive issue. Our own frame of reference is eIDAS and the EU, but these do not mark the limit of where we intend to operate.
The next Global Digital Collaboration Conference is scheduled for 7-9 September 2027, in Geneva. We’re looking forward to participating and contributing once again.